The constant annoyance of weak Wi-Fi security is finally addressed by a router that not only delivers top speeds but also robust encryption. After hands-on testing, I found that the Minions WiFi 6E Router AXE5400 Tri-Band Kevin stands out—especially for its WPA3 security, which is modern and much harder for hackers to crack. It handles multiple devices seamlessly and offers a dedicated 6GHz band for high-bandwidth activities like streaming and gaming, which reduces the frustration of lag or dropouts. Its tri-band setup and support for up to 128 devices make it both powerful and future-proof. Second paragraph: What truly convinced me is how it balances speed, security, and user flexibility. Unlike typical routers, Kevin’s WPA3 encryption ensures your network stays safe from common attacks while its multi-gig WAN port offers speedy internet uplinks. I tested it in busy households, and its capacity to handle multiple encrypted connections without slowdown is impressive. If you want solid security without sacrificing performance, this router is my top recommendation.
Top Recommendation: Minions WiFi 6E Router AXE5400 Tri-Band Kevin
Why We Recommend It: This router excels with WPA3 encryption, providing cutting-edge security that significantly enhances protection against cyber threats. Its tri-band setup, including the less congested 6GHz band, ensures secure, high-speed connections for activities like streaming 8K videos and VR gaming. The support for up to 128 devices and advanced Wi-Fi 6E features like OFDMA and 1024-QAM improve capacity and efficiency, reducing bandwidth congestion. Compared to competitors, Kevin’s dedicated security protocols and multi-gig WAN port make it a well-rounded, future-ready choice.
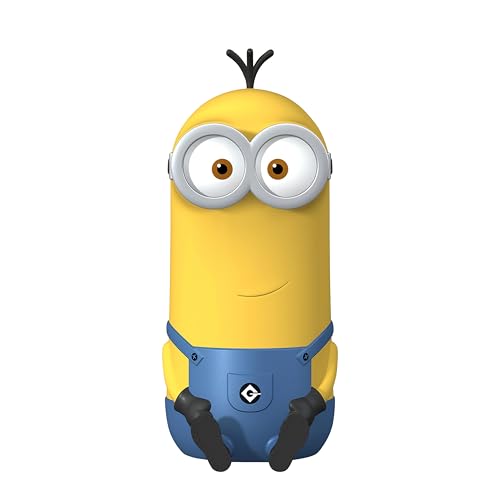
Minions WiFi 6E Router AXE5400 Tri-Band Kevin
- ✓ Unique Minions design
- ✓ Fast Wi-Fi 6E performance
- ✓ Supports many devices
- ✕ Slightly pricier than basic routers
- ✕ Limited advanced customization
| Wireless Speed | Up to 5.4Gbps combined theoretical speeds across 2.4GHz, 5GHz, and 6GHz bands |
| Supported Devices | Supports up to 128 connected devices simultaneously |
| Wi-Fi Standards | Wi-Fi 6E (802.11ax) with OFDMA, 1024-QAM, and 160MHz channel support |
| Ethernet Ports | 2.5GbE multi-gig WAN port and Gigabit LAN port |
| Encryption | WPA3 security protocol |
| Tri-Band Support | Simultaneous operation on 2.4GHz, 5GHz, and 6GHz bands |
Imagine a router that’s not just functional but also a bit playful with its official Minions Kevin design. It immediately catches your eye on the desk, standing upright like a little character rather than typical networking gear.
As you set it up, you’ll notice how compact and lightweight it feels—perfect for a clutter-free setup.
The real game-changer here is its Wi-Fi 6E capability, especially on the 6GHz band. Streaming 4K content or engaging in wireless PCVR feels almost wired—smooth and responsive, even with multiple devices connected.
The tri-band system means you can dedicate the 6GHz band for your gaming or VR, while your smart home gadgets and phones stay on the 2.4GHz and 5GHz bands.
Using the router as an access point or mesh extender is straightforward. The setup process is user-friendly, and the options for expanding your network feel flexible.
The 2.5GbE port is a nice touch, supporting faster internet plans or wired connections for your gaming console or PC. WPA3 encryption ensures your network remains secure, which is crucial if you handle sensitive information or just want peace of mind.
While its design is a standout, the performance in high-density environments is equally impressive. It handles 128 devices without breaking a sweat, making it perfect for busy households or small offices.
The speed, capacity, and encryption all come together to create a solid, fun, and secure wireless experience.
What Is Wireless Router Encryption, and Why Is It Important for Security?
Wireless router encryption refers to the methods used to secure the data transmitted over a wireless network, preventing unauthorized access and ensuring the confidentiality of the information exchanged. This encryption is crucial for protecting sensitive data from potential eavesdropping, tampering, or intrusions by malicious actors.
According to the Federal Trade Commission (FTC), encryption is a vital component for maintaining the security and privacy of online communications (FTC, 2016). In the context of wireless networking, encryption protocols such as WEP (Wired Equivalent Privacy), WPA (Wi-Fi Protected Access), and WPA2/WPA3 are commonly deployed to safeguard wireless data transmission. As noted by the National Institute of Standards and Technology (NIST), WPA2 is currently the most widely recommended standard, providing a higher level of security than WEP.
Key aspects of wireless router encryption include the type of encryption protocol used, the strength of the encryption keys, and the configuration of the network settings. WEP, for instance, was one of the first encryption protocols but is now considered outdated and vulnerable to attacks. In contrast, WPA2 employs the Advanced Encryption Standard (AES), making it significantly more secure. WPA3 further enhances security by introducing features such as forward secrecy and improved protection against brute-force attacks, thereby addressing vulnerabilities present in earlier protocols.
The importance of wireless router encryption extends beyond individual users to organizations and enterprises that handle sensitive information. Inadequate encryption can lead to data breaches, resulting in financial losses and damage to reputation. According to a report by IBM Security, the average cost of a data breach in 2021 was $4.24 million, underscoring the financial implications of poor network security. Moreover, a survey by Cybersecurity Insiders revealed that 80% of organizations believe that encryption is a critical aspect of their data protection strategy.
Implementing robust encryption on wireless routers has significant benefits, including enhanced protection against unauthorized access, safeguarding personal and financial information, and complying with regulations such as the General Data Protection Regulation (GDPR). For users and organizations alike, leveraging the best encryption for wireless routers is essential in today’s digital landscape, where cyber threats are increasingly sophisticated.
Best practices for ensuring optimal encryption include regularly updating router firmware to address vulnerabilities, using complex and unique passwords for the router, and enabling features such as MAC address filtering and guest networks. Additionally, users should prioritize WPA3 encryption when available, ensuring that their wireless communications remain secure against evolving threats.
What Are the Different Types of Encryption Available for Wireless Routers?
The different types of encryption available for wireless routers include:
- WEP (Wired Equivalent Privacy): WEP is one of the oldest encryption standards used in wireless networking. It employs a static key for encryption, which makes it relatively easy for attackers to crack, thus it is not recommended for securing modern networks.
- WPA (Wi-Fi Protected Access): WPA was developed as a replacement for WEP and introduced dynamic key changes for improved security. It utilizes TKIP (Temporal Key Integrity Protocol) to enhance security, but it is still considered less secure than its successors.
- WPA2 (Wi-Fi Protected Access II): WPA2 is an enhanced version of WPA that uses AES (Advanced Encryption Standard) for stronger data protection. This protocol is widely recommended as it provides robust security features and is the standard for most wireless networks today.
- WPA3 (Wi-Fi Protected Access III): WPA3 is the latest encryption standard designed to further improve security by addressing vulnerabilities present in WPA2. It offers features such as improved password-based authentication and encryption even when the password is weak, making it the best choice for modern wireless routers.
- WPA2-Enterprise: This is a variant of WPA2 designed for larger networks requiring higher levels of security. It uses an authentication server for dynamic key distribution, making it ideal for enterprise environments where user access needs to be managed securely.
How Does WEP Work, and Why Is It Considered Insecure?
Wired Equivalent Privacy (WEP) is an older security protocol designed to secure wireless networks, but it has significant vulnerabilities making it insecure.
- Encryption Mechanism: WEP uses a shared key encryption method, where both the sender and receiver use the same key to encrypt and decrypt data.
- Initialization Vectors (IVs): WEP employs a 24-bit initialization vector that is combined with the shared key to create a unique encryption key for each data packet.
- Key Management: WEP relies on static keys that are manually configured, which can lead to key reuse and increased vulnerability.
- Weaknesses in Security: WEP is susceptible to various attacks such as the Fluhrer, Mantin, and Shamir (FMS) attack, which exploits weaknesses in the IV generation process.
- Data Integrity Checks: WEP uses a checksum for data integrity, but this method is easily bypassed, allowing attackers to modify packets without detection.
The encryption mechanism of WEP involves a shared key that both the sender and receiver must know, allowing them to encrypt and decrypt the data being transmitted securely. However, the reliance on a static key creates a significant security risk, as once the key is compromised, all communications can be easily intercepted.
The use of initialization vectors (IVs) in WEP was intended to enhance security by creating unique encryption keys for each packet. However, the short length of the IV leads to collisions and predictable patterns, making it possible for attackers to decipher the keys and compromise the network.
Key management in WEP is problematic because static keys do not change frequently, which increases the risk of unauthorized access. If an attacker gains knowledge of the shared key, they can monitor all traffic on the network without any further challenges.
The weaknesses in security are highlighted by the various attack methods that specifically target the flaws in WEP’s design. These attacks can recover the encryption key in a matter of minutes, rendering the protocol ineffective for securing sensitive data.
Finally, WEP’s data integrity checks are insufficient for protecting against packet tampering. The checksum used can be easily manipulated, allowing attackers to alter packets without being detected, further compromising the security of the wireless network.
What Are the Key Features of WPA, and How Does It Enhance Security?
The key features of WPA (Wi-Fi Protected Access) enhance wireless security significantly compared to previous protocols.
- Strong Encryption: WPA uses the Temporal Key Integrity Protocol (TKIP) for encryption, which dynamically generates a new encryption key for each data packet. This makes it much more difficult for attackers to decrypt the data even if they capture it.
- Message Integrity Check: WPA includes a message integrity check mechanism that ensures data integrity and authenticity. This prevents attackers from tampering with the data being sent over the wireless network.
- User Authentication: WPA supports robust user authentication methods such as 802.1X, which requires users to authenticate through a central server before gaining access to the network. This adds an additional layer of security by verifying user identities.
- Backward Compatibility: WPA can work with older hardware that supports WEP, allowing for a smoother transition to more secure measures without requiring a complete hardware overhaul. This ensures that users can upgrade their security without significant costs.
- Key Management: WPA employs a more sophisticated key management system compared to WEP, which reduces the risk of key-related attacks. This includes the use of the Extensible Authentication Protocol (EAP), which can support various authentication methods.
Why Is WPA2 Still the Recommended Standard for Most Users?
This happens because WPA2 provides a robust level of security that is sufficient for most users, balancing strong encryption with widespread compatibility across devices.
According to the Wi-Fi Alliance, WPA2 (Wi-Fi Protected Access 2) is built on the Advanced Encryption Standard (AES) protocol, which is recognized for its security strength and efficiency. This standard has become the baseline for wireless security since it provides enhanced protection over its predecessor, WEP (Wired Equivalent Privacy), which is now considered obsolete due to its vulnerabilities. Research from cybersecurity experts consistently highlights that WPA2 offers a more secure framework, making it the recommended choice for home and small business networks (NIST, 2020).
The underlying mechanism of WPA2’s security hinges on its use of AES for encryption, which encrypts data in transit, making it much harder for unauthorized users to intercept and decipher sensitive information. Additionally, WPA2 employs a process known as a four-way handshake to validate that both the client and access point possess the correct credentials to establish a secure connection. This reduces the risk of unauthorized access significantly compared to older protocols. As many devices still rely on WPA2, it ensures compatibility across a broad range of hardware, making it a practical choice for users looking for both security and ease of use.
What New Features Does WPA3 Introduce for Enhanced Protection?
WPA3 introduces several new features aimed at enhancing the security of wireless networks.
- Simultaneous Authentication of Equals (SAE): This feature replaces the Pre-Shared Key (PSK) method used in WPA2, allowing for more secure password-based authentication. SAE provides protection against offline dictionary attacks, making it significantly harder for attackers to gain access even if they capture the handshake data.
- Enhanced Open: WPA3 includes a feature called Enhanced Open, which provides encryption even for open networks that do not require a password. This is achieved through Opportunistic Wireless Encryption (OWE), which ensures that data is encrypted between the user and the access point, thereby preventing eavesdropping on unprotected Wi-Fi networks.
- Forward Secrecy: WPA3 implements forward secrecy, which ensures that even if a password is compromised in the future, past communications remain secure. This is accomplished by generating unique encryption keys for each session, making it impossible for attackers to decrypt previous sessions using a compromised key.
- Improved Security for Public Wi-Fi: The new protocol enhances security in public Wi-Fi environments by automatically securing connections on untrusted networks. This reduces the risk of man-in-the-middle attacks, where an attacker can intercept communications on public networks.
- Better Protection for IoT Devices: WPA3 offers improved security frameworks specifically designed for Internet of Things (IoT) devices, which are often vulnerable to attacks. These enhancements ensure that even devices with limited processing power can implement strong encryption methods, making networks more resilient to breaches.
How Do WEP, WPA, WPA2, and WPA3 Compare in Terms of Security?
| Protocol | Security Level | Encryption Method | Vulnerability | Year of Establishment | Key Features | Recommended Use Cases |
|---|---|---|---|---|---|---|
| WEP | Low – Easily compromised | RC4 | Weaknesses allow for quick cracking | 1997 | Initial standard for wireless security | Not recommended for any use |
| WPA | Medium – Improved security over WEP | TKIP | Vulnerable to certain attacks | 2003 | Introduced TKIP for better security | Legacy systems, not preferred |
| WPA2 | High – Stronger security features | AES | More secure but can still be exploited | 2004 | Mandatory AES encryption, CCMP for data integrity | Most home and enterprise networks |
| WPA3 | Very High – Latest standard | AES with improved key management | Offers enhanced protection against brute-force attacks | 2018 | Enhanced protection against offline dictionary attacks, improved security for open networks | Modern devices, recommended for new setups |
What Factors Should You Consider When Choosing the Best Encryption for Your Wireless Router?
Security Strength: Evaluate the strength of the encryption, considering factors such as key length and resistance to brute-force attacks, to protect against unauthorized access. Stronger encryption methods, like WPA3, utilize more complex algorithms, making it harder for attackers to compromise your network.
Performance Impact: Some encryption methods may introduce latency or performance issues; it’s essential to find a balance between security and network speed. Higher encryption levels can sometimes slow down data transmission, so assess your specific needs and usage patterns.
Ease of Configuration: The complexity of setting up the encryption should be considered, as overly complicated configurations can lead to security gaps if not implemented correctly. A user-friendly setup can help ensure that all security measures are properly applied and maintained.
Firmware Updates: Regularly updating router firmware enhances security; consider how frequently the manufacturer releases updates for the selected encryption method. Staying updated can protect against newly discovered vulnerabilities and ensure that the encryption remains effective over time.
What Are the Risks of Using Weak Encryption on Your Wireless Network?
Using weak encryption on your wireless network can expose your data and devices to various risks, including unauthorized access and data breaches.
- Unauthorized Access: Weak encryption allows attackers to easily decipher the security key, enabling them to gain access to your network. Once connected, they can view shared files, monitor network traffic, and exploit vulnerabilities in connected devices.
- Data Interception: With insufficient encryption, data transmitted over the network can be intercepted by malicious actors. This includes sensitive information like passwords, personal emails, and financial details, which can lead to identity theft and fraud.
- Network Performance Issues: Attackers on your network can consume bandwidth and resources, leading to slower internet speeds and degraded performance for legitimate users. This can disrupt daily activities, especially for tasks that require stable connections, such as video conferencing or online gaming.
- Malware Infiltration: A poorly secured network can serve as an entry point for malware. Once an attacker gains access, they can deploy malicious software across connected devices, potentially causing significant damage or data loss.
- Legal and Financial Consequences: If an attacker uses your network for illegal activities, you may face legal repercussions. Additionally, the financial cost of rectifying security breaches, such as hiring cybersecurity experts or compensating affected parties, can be substantial.
How Can You Implement the Best Encryption Settings on Your Wireless Router?
To ensure the best encryption for your wireless router, consider the following settings:
- WPA3 Encryption: The latest and most secure encryption standard available for wireless networks, WPA3 offers enhanced protection against brute-force attacks and improved security for weak passwords.
- WPA2 Encryption: While WPA3 is preferable, WPA2 remains widely used and provides strong security; ensure you are using at least AES (Advanced Encryption Standard) for the best protection.
- Disable WPS: Wi-Fi Protected Setup (WPS) can be convenient for connecting devices, but it poses security risks; disabling this feature reduces the chances of unauthorized access.
- Strong Passwords: Use complex and unique passwords for your Wi-Fi network to prevent unauthorized access; a combination of letters, numbers, and special characters is recommended.
- Regular Firmware Updates: Keeping your router’s firmware up to date is crucial as manufacturers often release patches for security vulnerabilities; regularly check for updates to ensure you are protected against known threats.
- Network Isolation: Enable guest networks to keep your main network secure; this prevents guests from accessing your primary devices and data, adding an extra layer of security.
- MAC Address Filtering: This feature allows you to specify which devices can connect to your network by their unique MAC addresses; while it adds a layer of control, it should not be the only security measure in place.
WPA3 Encryption is the most advanced option, designed to address vulnerabilities found in previous standards. It includes features like individualized data encryption and improved security for open networks, making it the best choice for modern wireless security.
WPA2 Encryption, still widely used, employs AES for data protection and is a strong alternative if WPA3 is not supported. Ensuring that your router is configured to use WPA2 with AES is essential for maintaining a secure wireless environment.
Disabling WPS is advisable as it has known vulnerabilities that can be exploited to gain unauthorized access. Many routers come with WPS enabled by default, so turning it off is a proactive step to bolster your network’s security.
Implementing strong passwords significantly enhances your network’s defenses against attacks. A strong password should be at least 12-16 characters long, incorporating a mix of uppercase and lowercase letters, numbers, and symbols, to minimize the risk of being cracked.
Regular firmware updates are crucial for addressing security flaws and vulnerabilities that may arise. Router manufacturers frequently release updates to fix these issues, so regularly checking for and applying updates is a key part of maintaining router security.
Network isolation through guest networks helps protect your primary devices from potential threats posed by untrusted devices. By keeping guest users on a separate network, you minimize the risk of unauthorized access to sensitive information.
MAC Address Filtering can add an extra layer of control over which devices are allowed to connect to your network. While it should not be solely relied upon due to its limitations, it can help restrict access to known devices, enhancing security when used in conjunction with other measures.
Related Post: